
APAC firms race ahead on AI agents, but controls lag
Fri, 30th Oct 2026 (Today)
SailPoint has published research on the use and oversight of AI agents in Asia Pacific organisations, finding that most businesses using the technology have not put dedicated controls in place.
It found that 85% of APAC enterprises now run AI agents in production, but only 5% have deployed security tools designed to govern what those agents can access and do. The research also found that 95% of organisations in the region that have deployed AI agents are operating them without supervision.
The figures point to a widening gap between corporate adoption of AI agents and the controls used to manage them as a form of non-human identity. These systems can make decisions, access data and hold credentials, yet many businesses still lack clear oversight of ownership, permissions and behaviour.
According to the research, 68% of organisations across the region still rely on manual or ad hoc processes to manage non-human and AI agent identities. At the same time, 45% remain at the early stages of their identity security journey.
Detection of unsanctioned AI systems also appears limited, with only 30% of APAC enterprises having mature measures to detect shadow AI, defined as ungoverned and unauthorised agent deployments.
Control gap
The data comes as businesses face rising pressure to deploy AI in operational settings while regulators demand stronger controls over data access and cyber risk. In Australia, organisations are also navigating stricter expectations under privacy reforms and prudential standards such as APRA CPS 234.
Non-human identities have become a growing focus for security teams as companies automate more tasks and connect more systems. Unlike human staff accounts, these identities can include software agents, bots, service accounts and machine credentials that often operate continuously and at scale.
Where governance is weak, agents may retain access they no longer need, operate without a clearly assigned owner or make changes without timely review. The risk becomes greater when AI agents can retrieve information, trigger workflows or act across several systems.
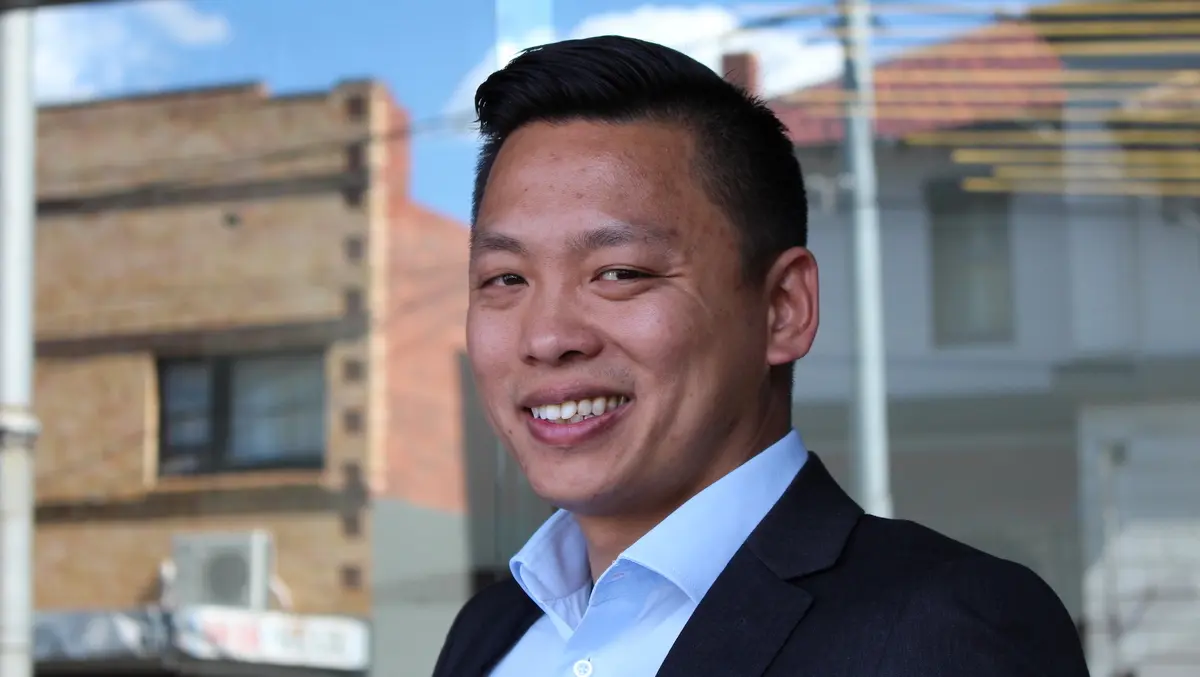
Nam Lam, Group Vice President, Australia and New Zealand, SailPoint, said: "Business leaders are under pressure to drive growth through AI, but the data shows governance hasn't kept pace. Most businesses in the region can't say who owns a given agent, what it can access, or whether it's still behaving as it should. That's an urgent problem at this scale, because one agent operating outside its boundaries can do a lot of damage before anyone notices. ANZ enterprises need to treat agent ownership and oversight as a condition of deployment, not something to sort out afterwards. Organisations must discover every agent in their environment, automate its identity lifecycle and grant permissions only when required."
Broader findings
The APAC figures sit alongside wider global findings on the commercial and insurance implications of identity controls. Globally, 62% of organisations that have invested in securing non-human identities reported measurable productivity gains.
Meanwhile, 76% of global leaders expect stronger identity governance to improve their eligibility for cyber insurance or affect the terms they can obtain. That suggests identity controls are being viewed not only as a technical safeguard, but also as a factor in broader risk management and operational resilience.
For companies expanding their use of AI agents, the challenge is no longer limited to deployment. The research suggests governance, monitoring and lifecycle management are lagging, particularly in organisations still dependent on manual processes.
That gap may become harder to sustain as AI agents take on larger operational roles and become more deeply embedded in customer service, internal administration and decision-making tasks. In that setting, weak oversight of non-human identities can create security and compliance issues that are difficult to trace once systems are already active.
The findings also underline a more basic problem for many businesses: visibility. If organisations do not know which agents exist, who is responsible for them and what permissions they hold, security teams may struggle to revoke access, investigate incidents or demonstrate compliance with internal policies and external rules.