

AppViewX expands Quantum Trust Hub for quantum migration
Thu, 5th Nov 2026 (Today)
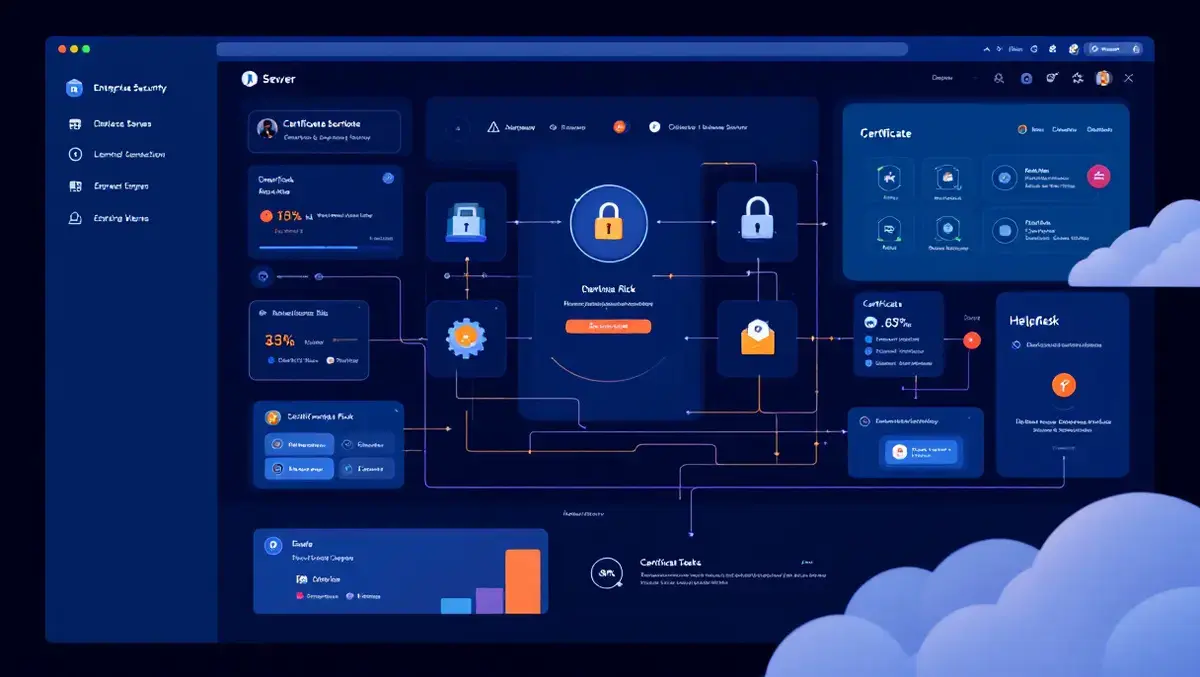
AppViewX has expanded its Quantum Trust Hub and made it available as a standalone product, targeting organisations preparing for post-quantum cryptography migration.
The added functions are designed to help security teams discover cryptographic assets, assess exposure to quantum-related weaknesses, prioritise risk and manage remediation through existing workflows.
Quantum Trust Hub now uses what AppViewX describes as an agentless-first approach, drawing on security tools already deployed in customer environments rather than relying mainly on new agents or sensors. A new integration with Qualys adds to existing support for Tenable, allowing users to identify cryptographic assets and configurations through those platforms.
Users can also upload Cryptographic Bills of Materials and Software Bills of Materials from third-party tools to create a single inventory of cryptographic assets. According to AppViewX, that inventory can span certificates, TLS configurations, cipher suites, keys and application code.
The launch comes as organisations face growing pressure to map their cryptographic exposure ahead of a broader shift away from older encryption standards. NIST finalised its first post-quantum cryptography standards in 2024 and has said it plans to begin phasing out RSA and ECC in 2030.
That timetable has added urgency for federal agencies and large enterprises with complex technology estates. Executive Order 14412 directs federal agencies to move high-value assets and high-impact systems to post-quantum cryptography for key establishment by 2030, with digital signature adoption to follow by the end of 2031.
Beyond certificates
AppViewX is positioning the updated product around a broader definition of cryptographic risk. Rather than treating certificate inventories as a complete view, it argues that exposure also sits in protocols, keys, configurations and software components, creating a more fragmented problem for security teams.
The platform classifies assets as quantum-vulnerable or quantum-resistant and applies business application context and NIST-aligned severity ratings to rank remediation priorities. Executive dashboards and continuous monitoring are intended to help teams track security posture and migration progress over time.
For remediation, findings can be sent directly into ServiceNow as tickets containing affected assets, identified risks, suggested fixes and ownership information. Tickets can also be grouped by remediation scope, which is intended to make it easier for teams to move from discovery to action.
Jennifer Glenn, Research Director at IDC, pointed to the immediate risks around cryptographic management as well as the longer-term shift to quantum-resistant systems.
"The quantum transition is a complex undertaking that enterprises need to start preparing for now," said Jennifer Glenn, Research Director at IDC. "Recent attacks involving compromised cryptographic credentials and signing keys underscore the risks organizations already face today. With federal migration deadlines approaching and quantum computing potentially advancing faster than expected, understanding the full scope of cryptographic exposure will be essential to planning an effective response."
Broader portfolio
The product update also fits into a wider effort by AppViewX to connect cryptographic discovery with its other identity security products. Quantum Trust Hub works alongside its certificate lifecycle management and SSH key lifecycle management products, which can be used when certificates or SSH keys need replacing as part of a post-quantum review.
AppViewX has also been extending its work in AI agent identity security. It said its agent identity product is intended to discover, govern and control the actions of AI agents at runtime, while its core certificate lifecycle management and PKI products can issue cryptographically verifiable, quantum-resilient identities for those agents.
AppViewX is among a growing group of cybersecurity suppliers trying to tie post-quantum planning to broader identity and infrastructure management. For customers, the immediate priority is less a full cryptographic swap-out today than establishing an inventory and governance process that can support migration as standards, deadlines or threats change.
Archit Lohokare, Chief Executive Officer of AppViewX, said the company sees continuous visibility as the starting point for that work.
"The quantum clock is ticking, and enterprises cannot afford to wait until post-quantum migration becomes an immediate requirement to understand their exposure," said Archit Lohokare, Chief Executive Officer of AppViewX. "Certificates are only one part of the equation. Cryptographic risk extends across the identities, keys, protocols, and applications that underpin enterprise trust. With Quantum Trust Hub, we're giving organizations the continuous visibility and risk intelligence needed to identify vulnerable cryptography, focus on their most critical exposures, and take a more proactive approach to quantum readiness."