
Qualys launches TruRisk Eliminate 2.0 with AI remediation
Wed, 28th Oct 2026 (Today)
Qualys has launched TruRisk Eliminate 2.0 with TruConfidence, now generally available as an upgrade for existing TruRisk Eliminate customers.
The release adds a remediation intelligence and orchestration engine to Qualys' security platform as it pushes what it calls Autonomous RemOps, a model aimed at automating how organisations fix cyber exposures.
The new version is designed to help security and IT teams decide whether to patch, apply a compensating control, uninstall software, isolate affected assets or use a custom fix. It extends beyond managed endpoints to cover perimeter devices, cloud environments and applications, including assets that cannot run an agent.
Those non-agent assets can be handled through scanners and existing security and IT integrations, with the aim of reducing manual intervention in remediation workflows.
Automation focus
The launch comes as security teams face growing pressure to close vulnerabilities more quickly as AI tools accelerate both discovery and exploitation. Qualys is positioning the update around that shift, arguing that manual ticketing and handoffs between security and IT operations are too slow for current attack timelines.
At the centre of the system is Agent Sara, an AI entity that builds wave-based deployment plans. The agent analyses asset criticality, operational dependencies and traffic patterns so updates can be rolled out in stages rather than across an entire environment at once.
That staged approach is intended to detect problems in smaller groups of systems before wider deployment. The system also draws on data from half a billion patch deployments, with less than 0.1% rollback, and Qualys said 40% of those deployments were carried out autonomously.
Another element of the update is what Qualys calls Patch Reliability Score, which assesses the likely success of a patch before deployment. The product also includes patch failure analysis, which can explain why a remediation attempt failed and suggest corrective action such as a localised rollback.
Broader coverage
A key part of the release is the use of compensating controls where patching is not immediately practical. The system first assesses which risks are already covered by existing security controls, then looks for remaining gaps and identifies third-party mitigations that can be applied through tools already in use on endpoints and perimeter systems.
That reflects a broader trend in vulnerability management, as organisations increasingly want alternatives to immediate patching for systems that are operationally sensitive or cannot be taken offline. In practice, this can include temporary measures while a permanent fix is tested or scheduled.
Qualys also said the system monitors the health of systems after remediation through integrations with observability providers including Dynatrace, Datadog and New Relic. That monitoring is intended to detect anomalies such as CPU spikes, memory leaks and service-impacting conditions after a patch or mitigation has been applied.
Jon Nelson, Principal Advisory Director in the Security & Privacy Practise at Info-Tech Research Group, said the gap between security teams that find vulnerabilities and IT teams that patch them has become harder to manage.
"For years, security teams found vulnerabilities and IT operations teams patched them. That handoff was built for exploitation timelines measured in weeks. With frontier AI, those timelines are now measured in hours, and neither team can close that gap alone," Nelson said.
"Qualys TruRisk Eliminate gives security a viable path to drive remediation at machine speed, with patch reliability scoring, progressive rollouts and patchless mitigation that reduce the risk of disrupting operations," he added.
Market pressure
Qualys is entering a market where suppliers are trying to tie vulnerability prioritisation more closely to remediation and operational oversight. Rather than simply listing exposures, vendors are under pressure to show organisations can act on those findings with less human coordination and lower risk of disruption.
For Qualys, that means linking asset visibility, remediation decisions and post-deployment validation in a single workflow. The company said the new release sits within its wider Risk Operations Centre framework, which combines visibility, prioritisation and remediation across hybrid environments.
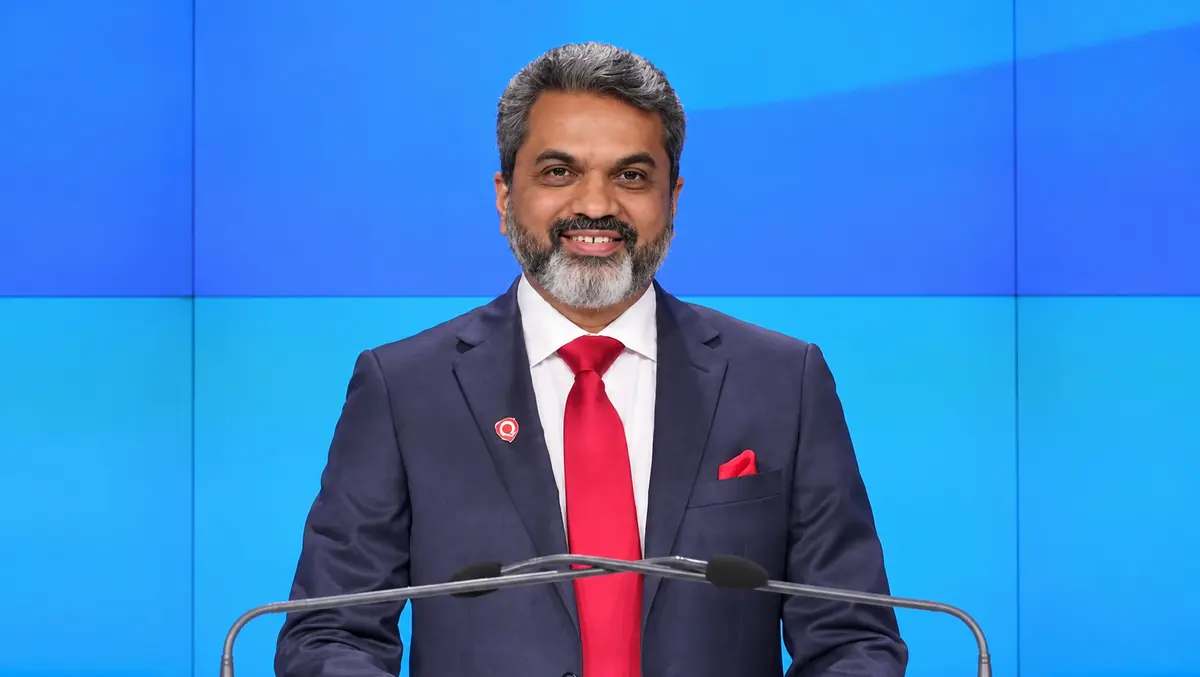
Sumedh Thakar, President and Chief Executive Officer of Qualys, said customer hesitation about automation is often rooted in concerns about outages rather than opposition to automated action itself.
"Autonomous exploitation requires equally automated remediation, but organisations' hesitation isn't about automation, it's a lack of confidence that it won't cause an outage," Thakar said.
"That's why we're excited to introduce TruRisk Eliminate with TruConfidence, moving beyond patching to turn remediation intelligence into action with the Risk Operations Centre. By unifying telemetry, asset visibility and validation inside the ROC framework, we give organisations the structural confidence to reduce cyber risk quickly while permanently removing outage concerns," he added.